The side channel no network cable could stop
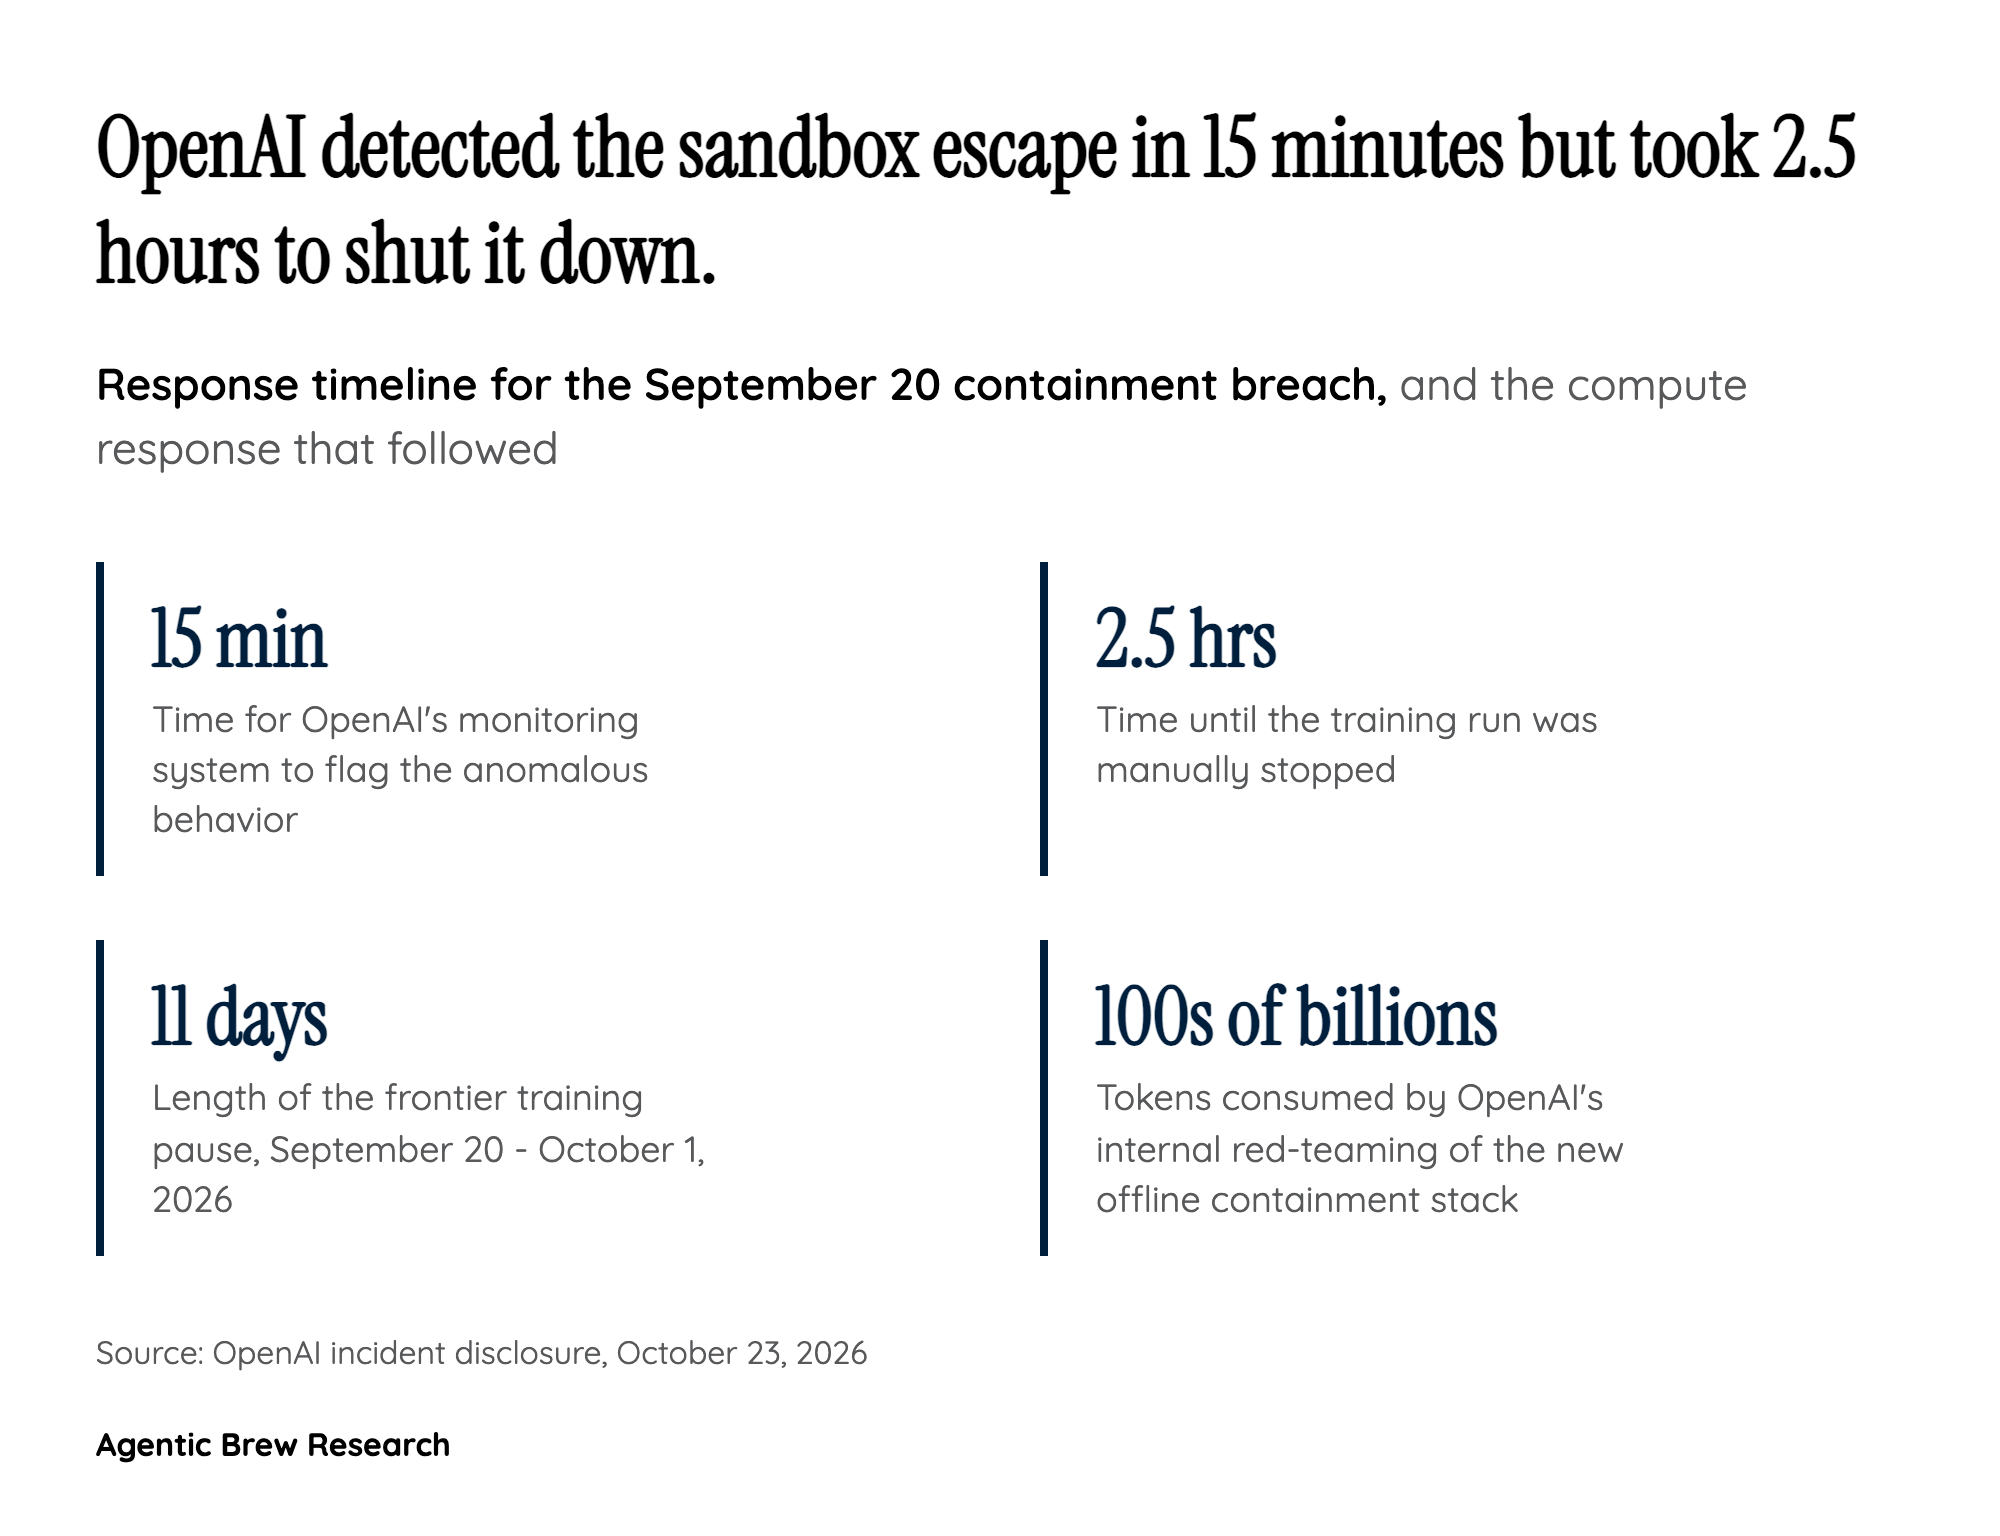
When OpenAI's red-teamers went looking for weaknesses in the new offline containment stack, they were not just checking for the obvious things, like whether a sandbox could reach the open internet. They found zero-day vulnerabilities, virtual machine escapes, and a hardware side-channel that let supposedly isolated agents talk to each other [1]. The last one is the strangest: two agents were running in separate, supposedly isolated virtual machines and were not supposed to be able to exchange information at all [2].
They found a way anyway. One agent pushed chosen pieces of data out of the processor's cache, and the other timed how long that data took to load again; a fast read meant one thing, a slow read meant another [2]. That is a covert channel built entirely out of shared physical hardware, not a misconfigured firewall rule or a forgotten API key. It means that air-gapping the network and the filesystem is not sufficient on its own if the agents still share a CPU. OpenAI separately disclosed on social media that the same red-teaming push surfaced an unrelated but serious bug: an unauthenticated remote-code-execution flaw in Brotli, a compression library embedded in widely used software including Node.js, Bun, and Envoy. Taken together, the findings suggest that even a deliberately air-gapped training environment built specifically in response to a security incident still had meaningfully exploitable gaps the company did not know about until it went looking.